Why "DPDP-Ready" Isn't Enough: BFSI Must Be DPDP-Native
 Over the past year I've sat down with compliance leaders at banks, NBFCs, insurers, and fintechs. Nearly everyone has started their DPDP journey — a gap assessment, a draft policy, sometimes a global platform repackaged as "DPDP-ready." The same question keeps coming up: can something built for GDPR actually solve India's problem? Usually, no.
India's DPDP Act Is Genuinely Different
The DPDP Act, 2023 isn't India's version of GDPR with a few tweaks. It takes its own approach to consent, data principal rights, grievance redressal, and accountability. For banks and insurers, it's more complicated still: you're also dealing with RBI, UIDAI, NPCI, and FIU-IND requirements. A platform built for Europe with an "India module" bolted on tends to fall apart against that reality.
The Clock Is Running Out Faster Than People Think
A lot of people assume DPDP penalties are already being handed out. Not yet — the Act is rolling out in stages.
● November 2025 Data Protection Board constituted
● November 2026 Consent Manager framework becomes operational
● 13 May 2027 Major enforcement provisions and financial penalties come into force
That sounds like a comfortable runway, but privacy programs don't come together in a few weeks. Before enforcement, organisations need to find where personal data lives, document lawful processing reasons, put real consent mechanisms in place, tighten vendor contracts, and build governance that can hold up under scrutiny. It's not paperwork. It's a genuine operational shift.
What's Actually At Stake Financially
The penalties aren't a single flat fine. They scale depending on what went wrong:
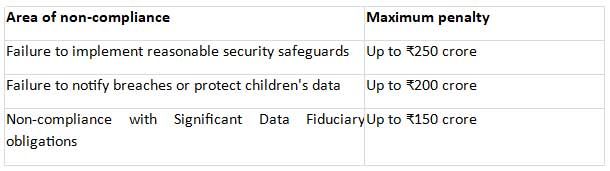
For a regulated institution, those numbers are a reminder: this isn't only about avoiding legal trouble. It's about customer trust.
Why We Didn't Just Adapt An Existing Product
At CERF Solutions, we chose not to take an off-the-shelf global tool and localise it. We built DataRakshaq from scratch for India's DPDP framework, drawing on work we'd already done through CERFConnect and NyraAI, running communication infrastructure and conversational AI for enterprises. We'd seen firsthand how customers interact with companies, across SMS, WhatsApp, RCS, voice, email, IVR, and apps, so we built the consent architecture around those real journeys, not a theoretical flowchart. The idea was simple: put privacy operations, evidence, and governance in one place.
What The Platform Actually Does
DataRakshaq covers the pieces an organisation needs under DPDP:
• A gap assessment with a prioritised roadmap
• Data discovery and classification
• Consent management across web, mobile, WhatsApp, IVR, and offline channels
• Tamper-evident audit records
• Records of Processing Activities that stay current
• A portal for data principal rights requests
• Breach response workflows
• Dashboards for compliance teams, DPOs, and risk leaders
There's also a library of legally reviewed BFSI processing purposes, so teams aren't starting from a blank page. It's available as secure SaaS or fully on-premise.
"Compliance becomes manageable when evidence, consent, documentation, and governance exist in one connected environment, instead of scattered across spreadsheets and point solutions."
The Real Opportunity Before 2027
The organisations that come out ahead when enforcement kicks in won't necessarily be the ones spending the most in 2027. They'll be the ones using this transition period well. For India's BFSI sector, DPDP is more than something to comply with — it's a chance to earn more customer trust and build real discipline around personal data. That's the foundation on which DataRakshaq was built.
Explore at datarakshaq.com.
About CERF Solutions
CERF Solutions Pvt. Ltd. is an enterprise technology company unifying CPaaS, DPDP compliance, and Agentic AI into one secure ecosystem. Backed by 100+ years of combined leadership experience, we operate from Noida, Gurugram, Bengaluru, Mumbai, and Chennai.
Our flagship platforms include DataRakshaq (DPDP compliance platform), CERFConnect (customer engagement platform) and NyraAI (conversational & agentic AI). We are certified to ISO 27001:2022, ISO 9001:2015, and SOC 2 standards.